Pentesting
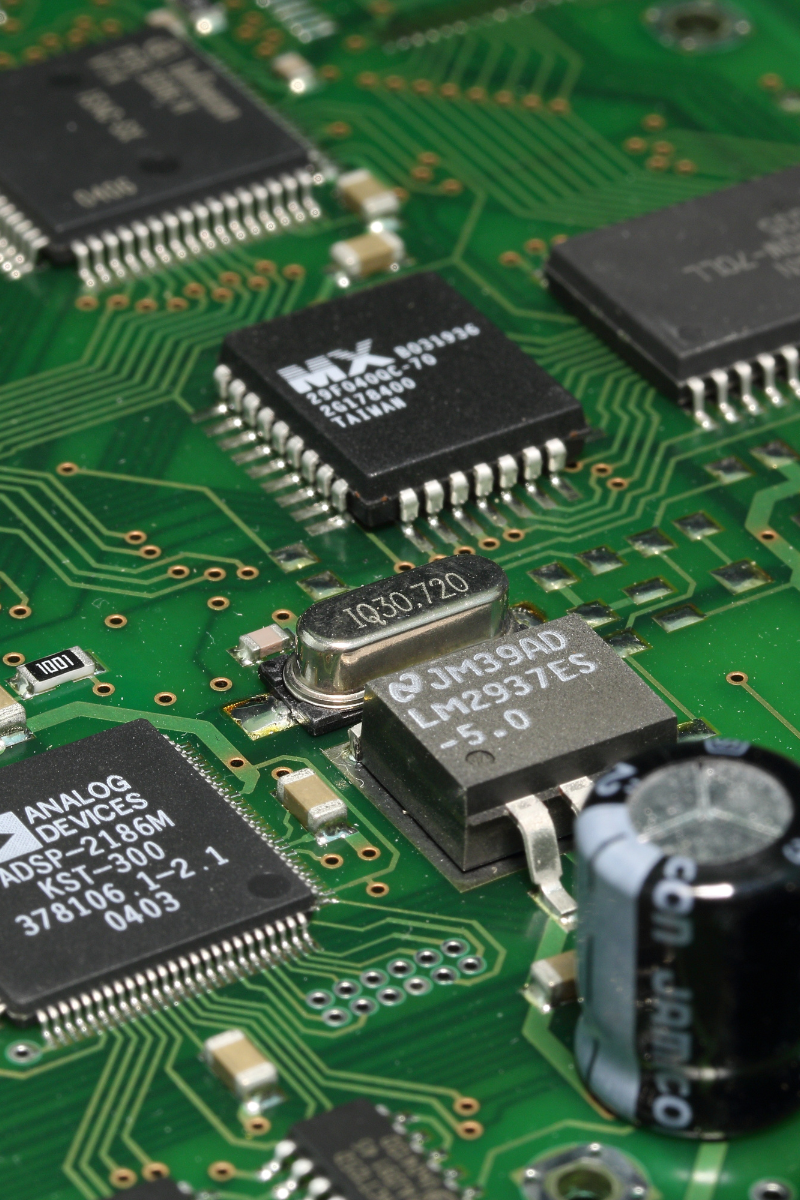
Hands-on testing of your hardware, firmware and software, with findings your engineers can act on.
Get your team and a security specialist together to map your product's biggest risks before launch.
You’re about to launch a connected product, and nobody has looked at it from an attacker’s point of view yet. A Pre-Launch Security Review brings your engineers and a security specialist together to find the biggest risks while there’s still time to fix them.
You share your architecture, code and documentation ahead of time (under NDA), and I review them before we meet. Then we spend a half or full day together, depending on the size of your system, walking through where your product is most likely to be attacked and what to prioritize. You’ll come away with a clear list of risks and recommended next steps.
Many teams use the review to plan their work before launch. If you need more depth, it can lead into a pentest or secure design work.
Launch coming up? Tell me about your product and timeline.
Hands-on testing of your hardware, firmware and software, with findings your engineers can act on.
Threat modeling and design review that build security in from the start, when changes are cheapest to make.
Give your engineers hands-on security skills through custom workshops and hacking challenges.